Archive
Research archive, page 3
Page 3 of 159 published articles on AI security, application security, supply chain, and real attack chains.
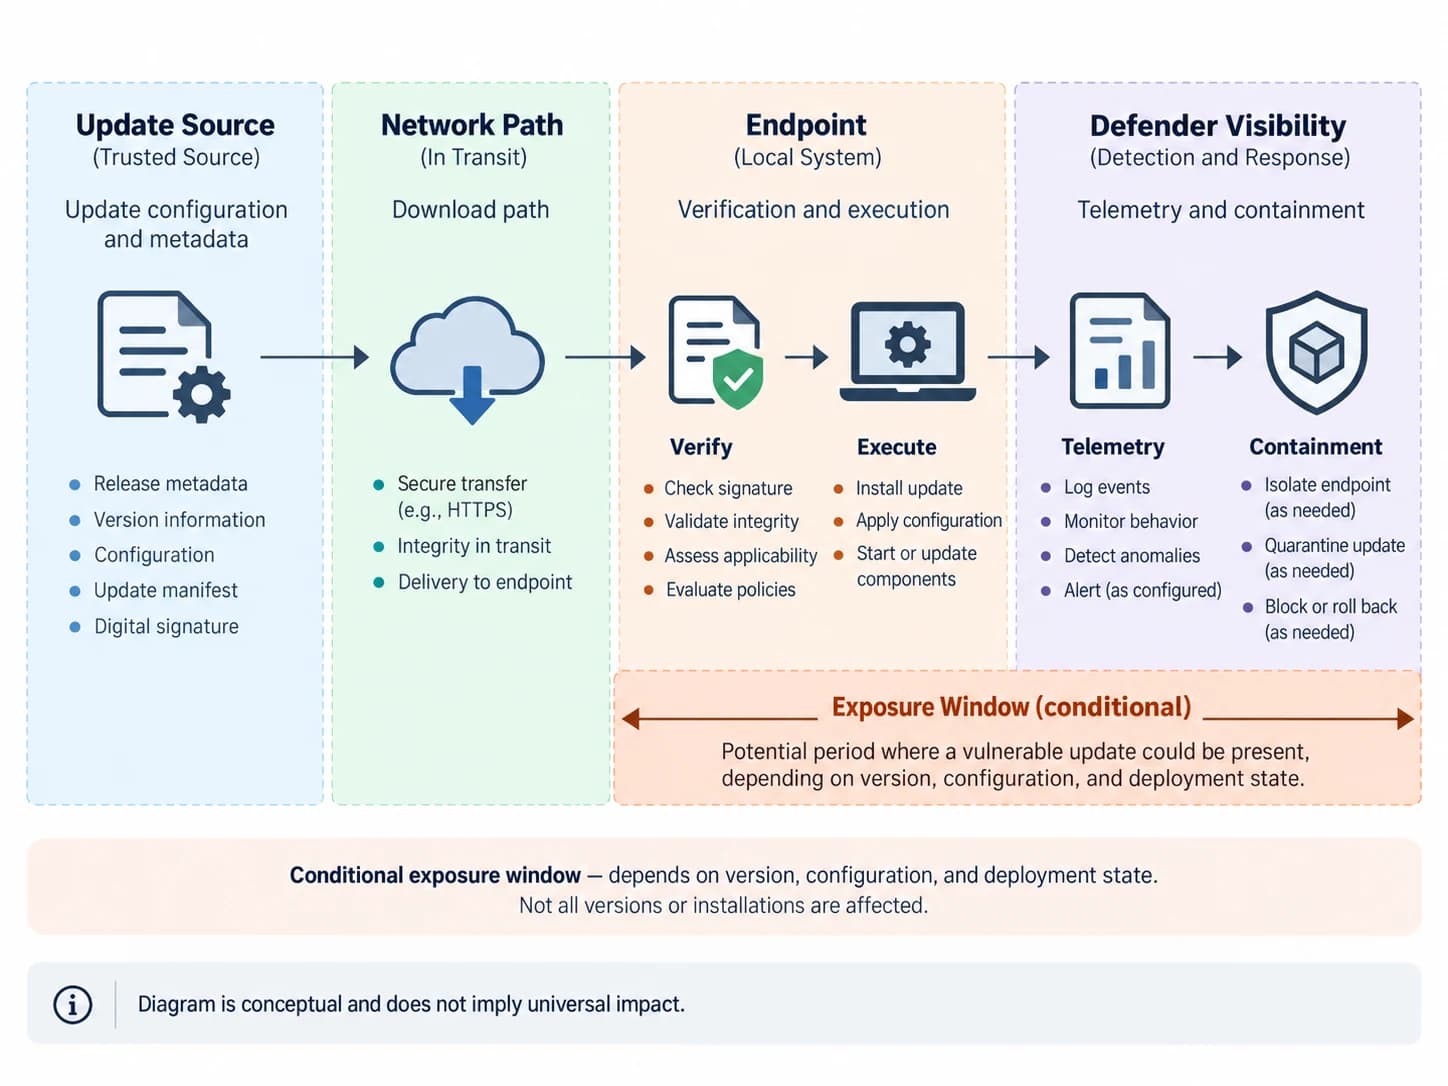
AOMEI Backupper Supply-Chain Incident: Evidence and Response
GTIG/Mandiant and ManageEngine documented brief AOMEI Backupper update tampering. Map endpoint exposure, evidence, and supply-chain controls.
File Upload Security: Testing the Pipeline End to End
A practical review of validation, parser isolation, storage, download authorization, scanning, and asynchronous upload pipelines.
SAML SSO Security Testing: Assertions, Signatures, and Tenant Mapping
A practical review of SAML assertion signatures, audience, recipient, replay, certificate rotation, and tenant provisioning.
Password Reset and Account Recovery Security Testing
A practical guide to account enumeration, reset-token design, email links, MFA recovery, support workflows, and session revocation.
GraphQL API Security Testing: Resolver Access, Batching, and Cost
A practical GraphQL assessment guide covering resolver and field authorization, batching, query cost, introspection, and error exposure.
DAST Findings Need More Than a Severity Score: HTTP Evidence and OAST Callbacks
A practical method for reviewing DAST findings with the request, response, scope, and out-of-band evidence that engineering needs to reproduce them.
Authenticated DAST Testing: Scope, Test Accounts, and Safe Scan Boundaries
Plan authenticated DAST without losing authorization boundaries: define hosts, identities, state-changing actions, exclusions, and retest conditions before a scan.
From AppSec Finding to Verified Fix: A Remediation and Retest Workflow
Turn a scanner or review result into a closed risk with ownership, impact context, a testable fix, evidence retention, and a scoped retest.
Agentic SAST Without Guesswork: File-Level Evidence, Validation, and Trace
How to review agent-assisted static analysis: inspect the pinned repository, source-to-sink path, exact code location, validation, and the limits of each finding.