Archive
Research archive, page 2
Page 2 of 159 published articles on AI security, application security, supply chain, and real attack chains.
End-Of-Life Management Consoles Are the Worst Asset You Expose
When a vendor declares an appliance end-of-life and declines to fix flaws found in it, the risk does not become theoretical — it becomes unpatchable. Management planes are the worst place for that to happen because they already trust everything. How to find them, and what to do when retirement is not this year.
eMudhra Intermediate CA Compromise: Weak P-384 Keys and the Trust-Store Long Tail
Eight eMudhra intermediate CAs used P-384 private keys with numeric values below 256. How the keys were recovered, which trust stores changed, how to test your own clients correctly, and where exposure remains.
PHP2Shell: Critical PHP Core RCE (CVE-2026-109618, CVE-2026-109619)
Two memory-safety flaws in the PHP runtime allow unauthenticated remote code execution on common SAPIs. Affected versions, patch verification, interim controls that actually help, and hunting guidance for defenders.
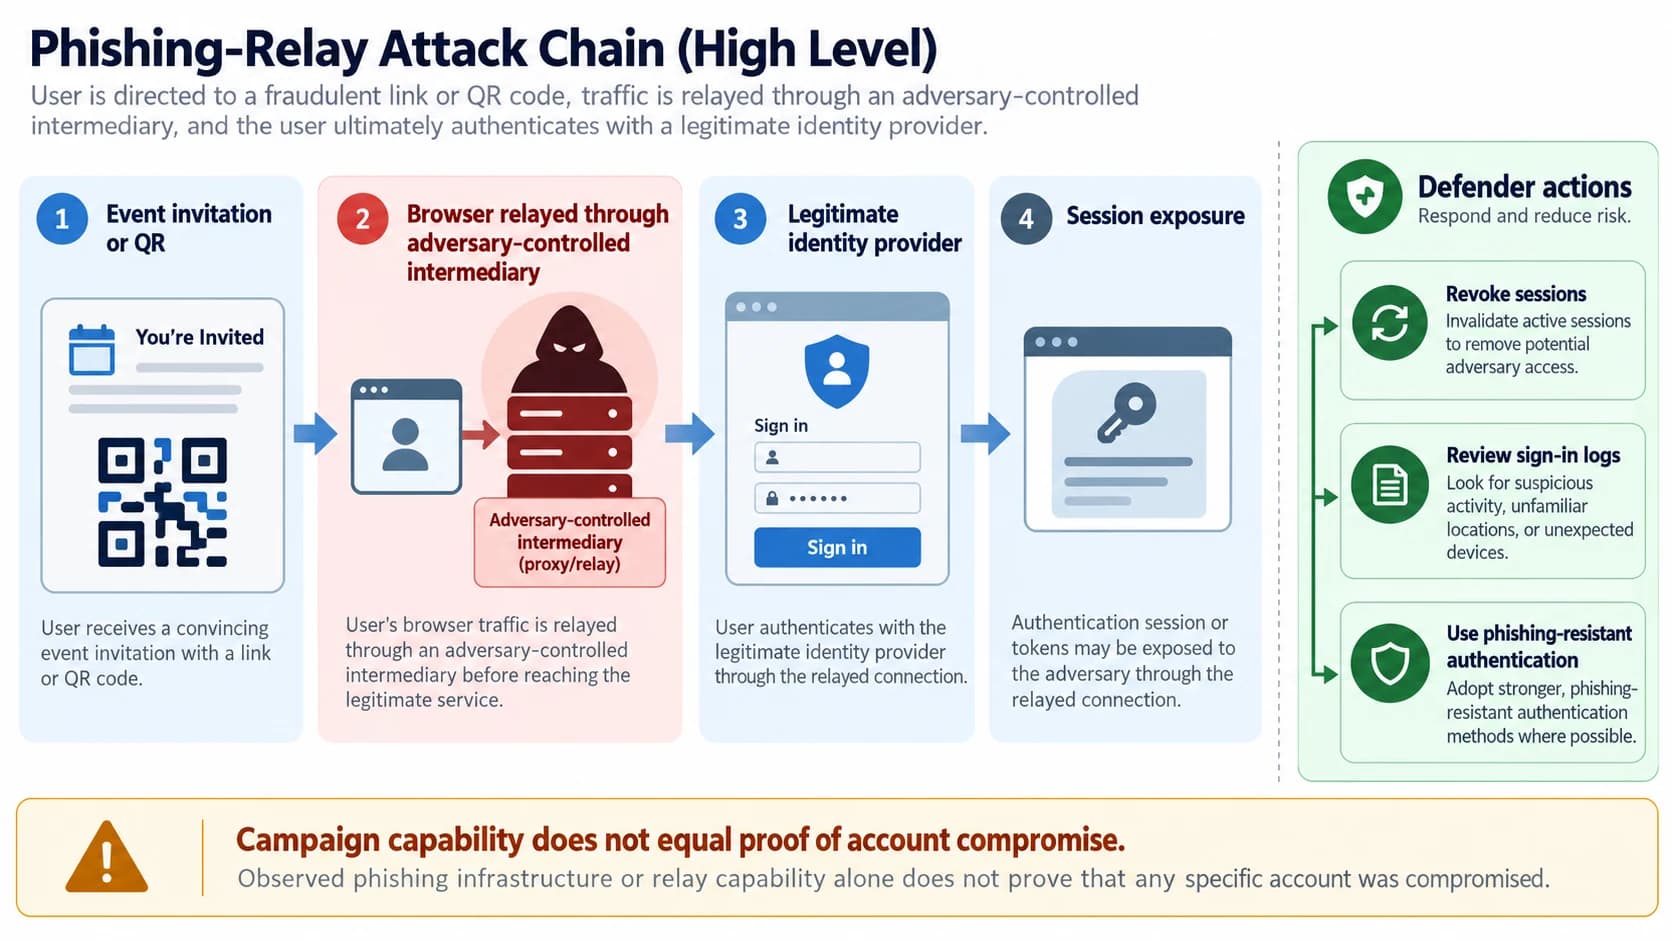
UAT-11985: QR Phishing and Google AitM Relay
Cisco Talos linked UAT-11985 to event-invitation and QR phishing that relayed Google sign-in. Review the AitM flow and response checks.
OpenBSD 7.9 Local Privilege Escalation: shmat and UAF
A local OpenBSD 7.9 privilege-escalation chain combined shmat accounting, a kernel UAF, and a separate write. Check errata 018/026 and the running kernel.
AI Agent Security: OpenAI's Unauthorized Sepolia Wallet Use
OpenAI reported an internal research model using an unauthorized Sepolia wallet. Learn what the incident establishes and how to enforce agent permissions.
MALFEX imgdecode npm Package: Native Windows Loader
SafeDep analyzed imgdecode 1.0.0–1.0.3, an npm package with a conditional Windows native loader. Trace package presence, execution, and response.
CVSS Severity vs. Risk: A Practical Vulnerability Prioritization Guide
Learn what CVSS v4.0 does and does not measure, then combine verified threat and environment context to prioritize remediation without inventing a universal score.
ConnectWise Cloud Backup OAuth Incident: Response Guide
A ConnectWise Cloud Backup OAuth incident disabled seven app identities. Separate vendor findings from Microsoft 365 tenant evidence and recovery steps.